Tech Vaidya WhatsApp Channel
Get AI updates, tech news, cybersecurity alerts and useful tech tips directly on WhatsApp.
Imagine waking up to find that the water flowing from your tap has suddenly stopped, or that the traffic lights across your entire city have simultaneously gone dark. While this sounds like the opening scene of a Hollywood disaster movie, it is rapidly becoming a chilling reality for communities across the United States. We are no longer living in an era where cybercriminals only care about stealing your credit card information or locking your computer files for ransom. A terrifying new chapter of cyber warfare has officially begun.
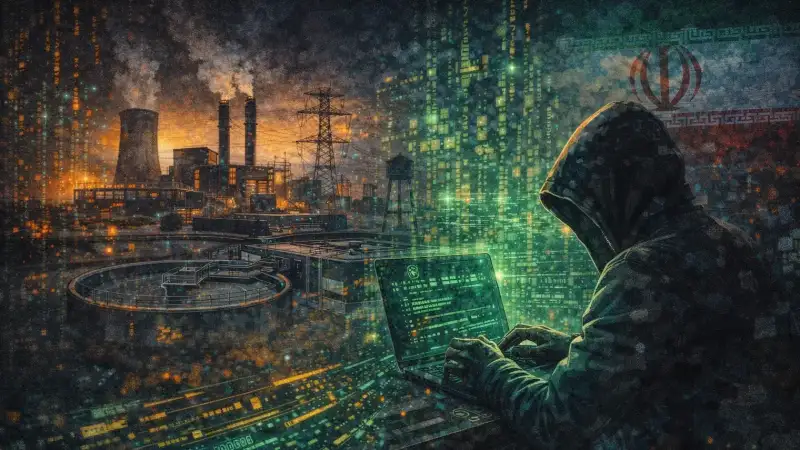
Today, hackers are actively bypassing traditional computer networks and aiming their digital weapons directly at the physical machines that keep American society functioning. In a highly unusual and alarming move, a coalition of the nation's top security agencies, including the FBI, CISA, and the NSA, has just dropped a bombshell joint security advisory. They have officially confirmed that hostile, foreign threat actors have successfully breached critical US digital borders.
According to the intelligence report, a sophisticated hacking collective affiliated with the Iranian government is currently launching a wave of aggressive attacks targeting American soil. Their primary goal is not financial extortion, nor is it intellectual property theft. Instead, these threat actors are operating with the sole, terrifying intent of causing severe, physical disruptions to the everyday lives of American citizens.
Hijacking the Lifelines of American Cities
The specific targets chosen by these Iranian-affiliated hackers are enough to keep national security experts awake at night. They are not going after social media companies or retail giants. Instead, the joint advisory reveals that these cybercriminals are directly attacking Government Services and Facilities, heavily impacting local municipalities. Even more alarming, they have successfully infiltrated the nation's highly sensitive Energy Sectors and essential Water and Wastewater Systems.
By targeting these specific domains, the hackers are essentially aiming at the vital organs of the American infrastructure. To execute these attacks, the threat actors are completely ignoring standard IT networks—the places where emails are sent and documents are stored. Instead, they are utilizing advanced techniques to locate and exploit internet-connected Operational Technology (OT) devices. This shift from IT to OT is what makes this current wave of attacks so incredibly dangerous.
But what exactly is Operational Technology, and why is it so vulnerable? Unlike standard office computers, OT refers to the specialized industrial hardware and software that directly monitor and control physical processes. They are the digital brains behind the heavy machinery that pumps fresh water into cities, controls the flow of electricity across the grid, and manages the intricate valves of wastewater treatment plants.
The Terrifying Science Behind SCADA and PLC Attacks
 Why Is Typing Kannada on Apple Laptops Still So Difficult? Which Kannada Keyboard Is Best for Apple Computers?
 Apple Finally Folded the iPhone! Why the iPhone Duo Could Change the Smartphone Industry
 TechVaidya: One Year. Over a Thousand Articles. And a long road still ahead...
 NASA Invites ISRO to Join the Moon Base Mission: Why This Could Be a Turning Point for India
 Toxic Review: Yash Owns the Screen, But Does the Film Own the Story?
To understand how a hacker sitting thousands of miles away can disrupt an American water plant, we must look at the specific equipment being targeted. The intelligence agencies highlighted that the attackers are actively exploiting Programmable Logic Controllers (PLCs), specifically those manufactured by industry giants like Rockwell Automation and Allen-Bradley. A PLC is essentially a ruggedized, miniature industrial computer designed to receive data from sensors and send commands to physical machinery, like telling a massive turbine to spin faster or a pipeline valve to shut completely.
Decades ago, these industrial control systems were physically isolated; they were never meant to be connected to the public internet. However, in the modern push for efficiency and remote monitoring, many facilities carelessly connected these critical PLCs directly to the web. This modernization inadvertently created a massive, glaring backdoor. The Iranian hackers are now scanning the internet, identifying these exposed industrial devices, and quietly slipping past the perimeter defenses.
Once inside the network, the attackers focus their efforts on manipulating the Human Machine Interface (HMI) and SCADA (supervisory control and data acquisition) displays. These are the screens that human operators look at to ensure the machinery is running safely. By injecting malicious code, the hackers can alter the project files within the PLCs, forcing the machines to behave erratically. Terrifyingly, they can also manipulate the data displayed on the operator's screen, making it look like everything is functioning perfectly normal while the machinery silently tears itself apart in the background.
Real Disruptions and The Dawn of Kinetic Cyber Warfare
The joint advisory issued by the FBI and NSA is not merely a theoretical warning about what might happen in the future. The agencies starkly admitted that multiple organizations across various critical infrastructure sectors within the United States have already fallen victim to these attacks. The malicious interactions with the industrial project files successfully triggered the exact chaos the hackers intended to create.
While the federal government has kept the specific names of the victimized cities, water facilities, and energy companies highly confidential to protect national security, they confirmed the grim reality of the situation. In several documented cases, this Iranian hacking activity resulted in severe operational disruptions and massive tangible financial losses. American infrastructure was physically impaired by lines of code deployed from across the globe.
This alarming development signals a permanent and terrifying shift in global conflict. We have officially crossed the threshold from the era of digital data theft into the era of kinetic cyber warfare, where a keyboard strike can cause physical, real-world damage. The fact that local municipalities and vital water sectors were left vulnerable exposes a critical weakness in how American infrastructure is currently guarded and maintained.
The urgent warning from the intelligence community serves as a final wake-up call for critical infrastructure operators nationwide. Relying on basic firewalls and outdated passwords is no longer a viable defense strategy. Industrial systems must be heavily audited, updated, and ideally, air-gapped entirely from the public internet. If organizations fail to heed this warning and secure their operational technology immediately, the next wave of cyberattacks could plunge entire cities into chaos, proving that the frontlines of modern war are now hidden within the wires of our own cities.
❤️ Also Read
❤️In a Hospital, 'Critical' Means Danger; To Scientists, It's a New Birth!
❤️The 'Breeder' Magic: A Reactor That Generates More Fuel Than It Consumes!
❤️Forget the iPhone 18 Pro: This 7.8-Inch Foldable Dummy Model Changes Everything!
❤️Android 15 Under 10K? Lava Bold N2 Pro 4G India Launch at 12 PM Today
❤️The AI Money Trap: Open Source Wins, Closed Source Loses
❤️The AI App Illusion: Why Free Artificial Intelligence is Bankrupting Silicon Valley?
❤️OnePlus India CEO Steps Down Amidst Global Arrest Warrant for Pete Lau: What Happens Next?
❤️Digital Betrayal: 1,530 Broken Rain Gauges Robbing Karnataka Farmers of Insurance!
❤️Tragedy on a Reel: How a Teen's Fatal Stunt in Hubballi Exposes the Dark Side of Digital Addiction
❤️Is ChatGPT Losing Its Sanity? The Dark Side of OpenAI's New 'Adult Mode' Plans
🟢 Follow our WhatsApp Channel JOIN ➤
🛒 ಆನ್ಲೈನ್ ಶಾಪಿಂಗ್ ಮಾಡುವಾಗ ಈ ಕೆಳಗಿನ ಲಿಂಕ್ ಬಳಸಿ
No Comment Yet.
Stay informed with breaking news, trending stories, and in-depth analysis.