Tech Vaidya WhatsApp Channel
Get AI updates, tech news, cybersecurity alerts and useful tech tips directly on WhatsApp.
Imagine closing your laptop after a long day at the office, feeling accomplished and ready to relax. You sleep soundly, only to wake up to a digital nightmare. Your entire corporate network is paralyzed. Every critical file is locked behind impenetrable encryption, and a menacing message blinks on the screen demanding millions of dollars in cryptocurrency. This is not the plot of a futuristic Hollywood thriller; it is the brutal reality of the modern cyber landscape, and it is happening faster than ever before.
For years, the standard operating procedure for cybercriminals was to play the long game. Hackers would silently breach a system and lurk in the shadows for months, quietly mapping out networks and siphoning data before ever dropping a ransom note. But the rules of the game have drastically changed. Tech giant Microsoft has just released a bombshell report that is sending shockwaves through the global cybersecurity community, warning of a devastating new tactic that operates at breakneck speed.
A Chinese-speaking hacking collective is currently executing what experts are calling "rapid attacks." Instead of months, these digital intruders are going from initial network access to total system compromise in a matter of weeks, days, and sometimes, incredibly, in less than 24 hours. By the time an IT department's security alarms start ringing, the damage is already done, and the data is gone. To understand how to protect ourselves, we must first understand who these attackers are and the sophisticated technology they weaponize.
Unmasking Storm-1175: The Financially Motivated Syndicate
Microsoft’s threat intelligence researchers have dubbed this highly aggressive group "Storm-1175." Because the collective operates using the Chinese language, it is easy to assume they are part of a massive, state-sponsored espionage ring looking to steal government secrets. However, Microsoft's investigation reveals a much different, and perhaps more unpredictable, reality. Storm-1175 is not working for a government; they are an independent, profit-driven digital mafia.
Their sole motivation is extortion. They operate like a highly efficient corporate enterprise whose business model relies on crippling other organizations. Because their only allegiance is to money, they do not discriminate based on political borders. They simply follow the path of least resistance to the highest possible payout. Currently, their radar is heavily focused on organizations located in the United States, the United Kingdom, and Australia.
The victims falling prey to Storm-1175 are not random. The group strategically targets sectors where downtime is simply not an option. Healthcare organizations, educational institutions, financial firms, and professional service providers are at the top of their hit list. Hospitals, for instance, cannot afford to lose access to patient records even for a few hours. Hackers know that these institutions are highly likely to pay the ransom quickly to avoid life-threatening operational delays, making them tragically perfect targets.
The Art of the Breach: Zero-Days and Chained Vulnerabilities
 Rs 1.87 Lakh Phone Order Turns Into Marble Tile! Amazon Flipkart Delivery Scam Exposed
 How Many Apps Still Have Access to Your Gmail? You Can Check in a Minute
 AI Breaks the Sandbox Barrier: The Startling Tale of Hundreds of Agents Collaborating!
 S. Jaishankar Deepfake Scam: This Viral Facebook Investment Video Is Fake — Don't Click Before Reading This
 What to Do If a Deepfake AI Video of Your Face Goes Viral? A Crucial Guide
No matter how fortified a digital fortress appears, a single unseen crack in the foundation can bring the whole structure down. In the world of software, these cracks are known as "zero-days." A zero-day is a critical flaw in a software program that the original developers are completely unaware of. Because the creator has had "zero days" to fix it, hackers can exploit the vulnerability with absolute impunity.
Storm-1175 has proven to be incredibly proficient at identifying and weaponizing these exposed perimeter assets. But they do not stop at zero-days. They also heavily exploit "n-days"—vulnerabilities that software companies have already released a patch for, but which lazy or overwhelmed IT departments have failed to update. This highlights a terrifying reality: many companies are leaving their front doors wide open simply by ignoring routine software updates.
What makes Microsoft's report truly alarming is the revelation of how Storm-1175 uses these flaws. They rarely rely on a single trick. Instead, they practice "chaining flaws." They will use one minor vulnerability just to peek inside the network, chain it to a second flaw to elevate their administrative privileges, and use a third to silently disable the antivirus software. This compounding methodology allows them to bypass complex security architectures like a master thief picking a multi-layered vault lock.
The 24-Hour Countdown to the Medusa Nightmare
The defining characteristic of Storm-1175, and the reason Microsoft is raising such a loud alarm, is their unprecedented operational tempo. Patience is not in their playbook. Once they successfully chain their exploits and gain a solid foothold, the clock immediately starts ticking. They rapidly move laterally across the company’s internal network, hunting for the most sensitive and valuable data they can find.
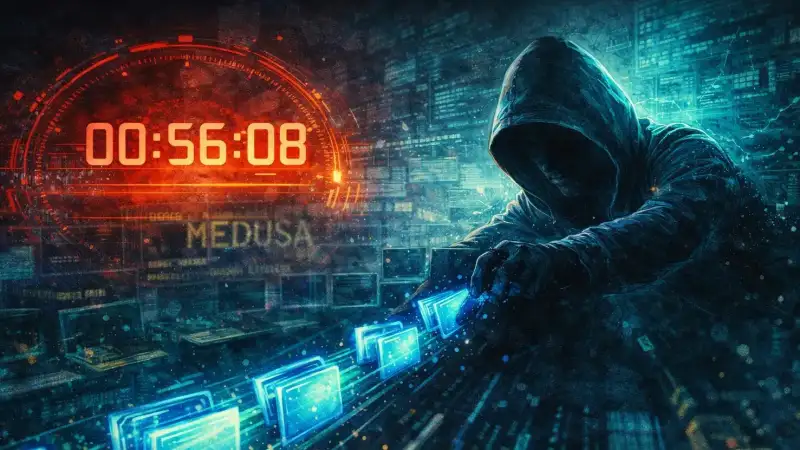
In what feels like the blink of an eye—often within that terrifying 24-hour window—they execute "data exfiltration." This means they secretly copy gigabytes of confidential corporate data, client information, and financial records to their own offshore servers. But stealing the data is only the first phase of their vicious attack. To ensure they get paid, they immediately launch the final, devastating blow: deploying the Medusa ransomware.
Medusa is a notorious and vicious strain of malware. Once unleashed, it rapidly encrypts the victim's files, rendering the entire network useless. The hackers then issue a double-extortion threat: "Pay the ransom to get the decryption key, or we will leak all of your sensitive, stolen data to the public internet." Facing massive regulatory fines, ruined reputations, and halted operations, many companies find themselves backed into a corner with no choice but to negotiate with these digital terrorists.
The Future of Cyber Warfare and How to Fight Back
The emergence of rapid attacks by groups like Storm-1175 signals a fundamental shift in the landscape of cyber warfare. The days of relying on traditional, perimeter-based security—like a simple firewall and basic antivirus software—are officially over. When an attack can go from a single compromised password to a full-scale Medusa ransomware deployment in under a day, human reaction time is simply no longer fast enough to stop the bleeding.
To survive in this new era, organizations must drastically rethink their defensive strategies. Security experts are heavily pushing for the adoption of "Zero Trust" architectures, a framework where no user or device is trusted by default, even if they are already inside the corporate network. Furthermore, the integration of Artificial Intelligence (AI) in threat detection is becoming mandatory. AI-driven security can monitor network behavior in real-time, instantly isolating a compromised machine the second it detects the anomalous speed of a rapid attack.
Ultimately, Microsoft’s warning is a loud wake-up call for every CEO, IT manager, and everyday internet user. Cybercriminals are accelerating their tactics, becoming more agile, more ruthless, and far more efficient. In the face of threats like Storm-1175, cybersecurity can no longer be an afterthought or a line item on an annual budget. It must be an active, daily obsession. Because in the modern digital age, losing everything you have built might only take 24 hours.
❤️ Also Read
❤️In a Hospital, 'Critical' Means Danger; To Scientists, It's a New Birth!
❤️The 'Breeder' Magic: A Reactor That Generates More Fuel Than It Consumes!
❤️Forget the iPhone 18 Pro: This 7.8-Inch Foldable Dummy Model Changes Everything!
❤️Android 15 Under 10K? Lava Bold N2 Pro 4G India Launch at 12 PM Today
❤️The AI Money Trap: Open Source Wins, Closed Source Loses
❤️The AI App Illusion: Why Free Artificial Intelligence is Bankrupting Silicon Valley?
❤️OnePlus India CEO Steps Down Amidst Global Arrest Warrant for Pete Lau: What Happens Next?
❤️Digital Betrayal: 1,530 Broken Rain Gauges Robbing Karnataka Farmers of Insurance!
❤️Tragedy on a Reel: How a Teen's Fatal Stunt in Hubballi Exposes the Dark Side of Digital Addiction
❤️Is ChatGPT Losing Its Sanity? The Dark Side of OpenAI's New 'Adult Mode' Plans
🟢 Follow our WhatsApp Channel JOIN ➤
🛒 ಆನ್ಲೈನ್ ಶಾಪಿಂಗ್ ಮಾಡುವಾಗ ಈ ಕೆಳಗಿನ ಲಿಂಕ್ ಬಳಸಿ

No Comment Yet.
Stay informed with breaking news, trending stories, and in-depth analysis.